Whatsapp
Get a quote
Email Us
Call
Skip to content

Identify Active Directory Risks Before Attackers Do

Professional Active Directory Security Assessments in Canada

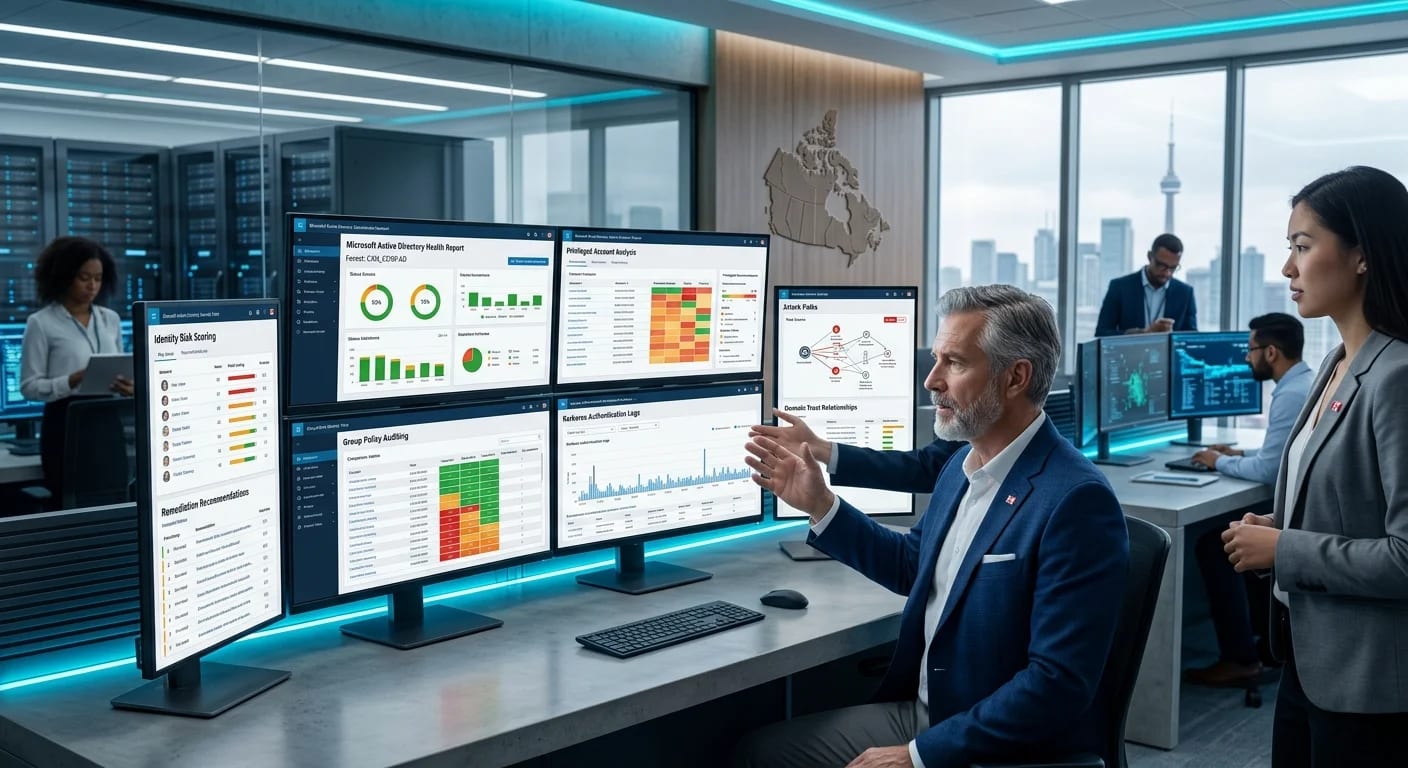
Your Active Directory environment controls access to critical systems, applications, and data across your organization. PlutoSec helps identify security gaps, validate security controls, and uncover risks that could be leveraged by attackers, enabling you to strengthen security and improve overall cyber resilience.

  • Certified Active Directory Experts

    CRTP and OSCP certified consultants specialize in Active Directory attack paths and privilege escalation.

  • Real World Approach

    We map your AD environment for misconfigurations attackers actively exploit to gain domain control.

  • Actionable Reporting

    Reports outline every attack path discovered with prioritized steps to close the gaps.

  • Confidential & Secure

    Domain credentials and infrastructure data remain confidential under strict access controls.

Professional Active Directory Security Assessments in Canada
About Us

Protecting Your Identity Infrastructure

Active Directory controls who can access what across your entire organization. When it is misconfigured or poorly managed, it becomes the fastest route to a full network compromise. Attackers do not need sophisticated exploits to take control. They use legitimate AD features, stale accounts, and permission misconfigurations that quietly accumulate over years of normal business operations.

At PlutoSec, we have worked with organizations across Canada and the United States to uncover these exact weaknesses. Our certified security professionals conduct thorough, manual first Active Directory security reviews that go far beyond automated scanning. We examine your AD environment the same way a skilled attacker would, then give you a clear, prioritized roadmap to fix what we find.

Reduce Alert Fatigue

Close Cybersecurity Skills Gaps

 Lower Total Security Costs

Improve Detection and Response Times

Get Started

Ready to Strengthen Your Cybersecurity?

Protect your business with expert led security assessments, penetration testing, and managed security services. Talk to our specialists today.

Book a Free Consultation

How Our Active Directory Security Review Works

  1. 1.

    Discovery & Scoping

    We identify the scope of the review, understand your Active Directory environment, and define assessment objectives.

  2. 2.

    Active Directory Assessment

    Our consultants evaluate configurations, permissions, group policies, privileged accounts, and security settings to identify risks.

  3. 3.

    Analysis & Validation

    All findings are reviewed and validated to determine their potential impact on your security posture.

  4. 4.

    Reporting & Recommendations

    Receive a detailed report with prioritized findings and actionable remediation guidance.

  5. 5.

    Remediation & Verification

    We help validate improvements and verify that identified security issues have been effectively addressed.

Why Choose Plutosec

Security Expertise That Delivers Results

Not all security reviews are equal. Many firms run automated tools against your environment and deliver a generic findings report. PlutoSec takes a different approach. Our team brings direct experience in adversarial techniques, incident response, and identity security to every engagement. We know what attackers look for because we simulate those attacks every day.

Active Directory Security Experts

Our consultants have extensive experience identifying security weaknesses, misconfigurations, and privilege related risks within Active Directory environments.

Comprehensive Security Assessments

We evaluate configurations, permissions, Group Policy settings, trust relationships, and privileged accounts to uncover security gaps.

Actionable Remediation Guidance

Every finding includes clear, prioritized recommendations to help strengthen security and reduce the risk of compromise.

Detailed Reporting

Receive comprehensive technical and executive reports with complete visibility into identified risks and remediation priorities.

What We Cover

Privileged Accounts & Permissions

Review administrative accounts, delegated privileges, and permission structures to identify excessive access and potential security risks.

Group Policy Security

Assess Group Policy Objects (GPOs) for misconfigurations, insecure settings, and opportunities to strengthen security controls.

Identity & Access Management

Evaluate authentication mechanisms, account management practices, and access controls to reduce the risk of unauthorized access.

Active Directory Configuration Review

Analyze domain configurations, trust relationships, organizational units, and security settings for weaknesses and misconfigurations.

Password & Account Security

Assess password policies, service accounts, stale accounts, and account management practices that could increase security risk.

Security Exposure & Attack Paths

Identify potential attack paths, privilege escalation opportunities, and configuration weaknesses that attackers could exploit.

Our Approach

  • Risk Based Assessment
  • Comprehensive Security Review
  • Attack Path Analysis
  • Actionable Recommendations
  • Active Directory Assessment
  • Attack Path Analysis
  • Identity & Access Validation

Tools & Technologies

  • BloodHound and SharpHound 
  • Impacket
  • Rubeus 
  • PowerView and PowerShell Empire Modules
  • CrackMapExec
  • Responder and Inveigh
  • Mimikatz 
  • PingCastle

Get Started

Ready to Strengthen Your Cybersecurity?

Protect your business with expert led security assessments, penetration testing, and managed security services. Talk to our specialists today.

Book a Free Consultation

Why Active Directory Security Matters

Protect Critical Systems

Secure the identity infrastructure that controls access to your most important systems, applications, and business resources.

Reduce Privilege Related Risks

Identify excessive permissions, misconfigured accounts, and privilege escalation opportunities that could be exploited by attackers.

Strengthen Identity Security

Validate authentication controls, account management practices, and security configurations to improve overall protection.

Prevent Unauthorized Access

Uncover vulnerabilities and attack paths that could allow threat actors to gain control of your environment.

CLIENT VOICES

What our clients say

5.0 / 5based on 20 verified reviews
GoodFirms

Their team conducted a thorough security assessment and penetration testing of our website, keeping us informed throughout the process. What really stood out was how they presented technical findings in straightforward language rather than jargon — our entire team could understand the vulnerabilities and risks without needing to decode complex terminology. The final report included practical remediation recommendations we could actually implement.

Rachel CohenOwner, StantVerified
GoodFirms

Their team used a hands-on approach to identify vulnerabilities and security weaknesses that automated scans had missed, risks that could have exposed sensitive user information. Each finding was clearly explained, prioritized by severity, and paired with practical remediation recommendations. They remained available to answer questions and guide us through remediation.

Adam KowalskiOwner, Viva-menteVerified
GoodFirms

Their team took the time to understand our sustainability platform, performed a thorough security assessment, and kept us informed throughout the engagement. The final report clearly prioritized each finding and included practical remediation steps that our technical team was able to implement without confusion, significantly improving our platform's security posture.

Luca MorettiIT Security Manager, GEA.viteVerified
GoodFirms

Their team conducted a thorough penetration test and security assessment, identified vulnerabilities across our infrastructure, and provided clear, actionable steps to address them. Communication was professional and responsive throughout, and the final report was detailed yet easy to understand without unnecessary technical jargon. We especially appreciated their hands-on approach and meticulous attention to detail.

Maya EllingtonIT Manager, Pescara Blu B&BVerified
GoodFirms

Their team strengthened our cloud infrastructure, improved our access controls, and addressed security risks while providing ongoing monitoring. Communication was consistently clear, their support was responsive whenever we needed it, and their recommendations were practical and straightforward to implement.

Julian MercerIT and Cybersecurity Director, NovellowinesVerified
GoodFirms

Their team uncovered vulnerabilities in our web application that we would have missed and explained each one clearly with practical remediation steps. They stayed responsive throughout the engagement and made the entire process straightforward.

Wyatt CallahanCEOVerified
GoodFirms

Their team continuously monitored our hospitality operations for vulnerabilities and threats, flagging potential issues early with clear recommendations before problems escalated. They were responsive and knowledgeable, making security guidance practical and actionable for our specific needs. They've become a trusted partner we rely on.

Riley EastwoodIT Manager, CrodadalagoVerified
GoodFirms

Their team conducted a thorough penetration test and vulnerability assessment of our web environment, uncovering vulnerabilities we'd missed entirely. They communicated findings clearly, provided practical remediation guidance we could actually implement, and remained professional and responsive throughout the engagement.

Ava WhitmoreDirector of IT Operations, IlpassaggioVerified
GoodFirms

Working with PlutoSec was smooth and professional from start to finish. Their team manually tested our WordPress website, clearly explained each vulnerability they found, and gave us actionable steps to fix them, which made remediation straightforward instead of overwhelming. They were responsive to our questions and guided us through the process.

Sara MahmoudCTO, Andrea BaccoliniVerified
GoodFirms

Their team took time to understand our website, conducted a thorough security assessment and penetration test, then clearly explained each vulnerability they found. They provided practical remediation guidance we could actually implement to address the findings and strengthen our defenses. Communication was responsive throughout, and we felt confident in their technical knowledge and approach.

Aisha RahmanIT Security Manager, IlmiobeautyVerified
GoodFirms

Their team conducted a detailed penetration test and vulnerability assessment, identifying security weaknesses and clearly explaining the business risks behind each finding. What impressed us most was their hands-on approach — they manually validated vulnerabilities rather than relying solely on automated scanning. Beyond the initial assessment, their managed security services helped us maintain stronger ongoing security.

Zoya KhanCTO, FProgettiVerified
GoodFirms

Their manual penetration testing caught vulnerabilities that automated scanners had missed, and their final report was detailed with practical remediation recommendations we could actually implement. The team demonstrated strong technical expertise and remained responsive throughout the project, answering our questions during remediation and completing everything on schedule.

Adam Al-MasriIT Manager, FoggiaitVerified
GoodFirms

PlutoSec provided proactive managed security, vulnerability management, and ongoing monitoring that meaningfully strengthened our security posture. The team was responsive and professional, addressing concerns quickly and giving us confidence that our systems and business data are properly protected.

AnonymousVerified clientVerified
GoodFirms

Their team helped us improve IT security, system reliability, and day-to-day support, while always being responsive when we needed assistance. We especially appreciated their practical approach, clear communication, and cybersecurity knowledge.

AnonymousVerified clientVerified
GoodFirms

Their cybersecurity team took time to understand our environment and performed a detailed penetration test, going beyond automated tools to manually validate findings and explain the potential business impact clearly. The final report was well-structured with practical remediation recommendations our team could easily follow.

AnonymousVerified clientVerified

Insights & Research

ThreatResearch,CVEAnalysis,andSecurityGuides

Hands on analysis from our engineers, current vulnerabilities, emerging attack patterns, and the security decisions shaping enterprise risk in 2026.

1 min readMay 23, 2025By Admin

Top Cybersecurity Company in Canada for Trusted Digital Protection

Cyber threats grow stronger and more frequent every day. You use the internet more than before. Hackers target your data through attacks, ransomware, and fake emails.

Read article
1 min readMay 30, 2025

Infrastructure Penetration Testing for Full-System Security Coverage

Protect your systems before hackers attack. Infrastructure penetration testing finds weak spots, ensures compliance, and helps keep your data safe.

Read
1 min readFeb 14, 2026

Cloud Security in 2026: What Businesses Must Know to Protect Data

Cloud security is evolving fast in 2026, and Canadian businesses need to be prepared. From new threats to compliance requirements, learn how to protect your cloud

Read

Frequently asked questions

Answers to the questions we hear most. Still unsure how it applies to your environment? Our engineers are happy to talk it through.

How long does an Active Directory security review take? 
Most AD security reviews are completed within five to ten business days, depending on the size of your environment. The scoping call at the start of the engagement helps us estimate the timeline accurately for your specific setup.
Do you need access to our production environment? 
Our review is conducted remotely and read only. We do not make any changes to your environment, and work within a controlled scope agreed upon during the scoping phase. The assessment is designed to have zero impact on your operations.
What is the difference between an Active Directory review and a penetration test? 
An Active Directory security review focuses specifically on the configuration, permissions, and health of your AD environment. A penetration test may include AD attacks as part of a broader network attack simulation. We offer both, and many clients start with an AD review to understand their identity security posture before proceeding to a full internal network penetration test.
We are running a hybrid Azure AD environment. Can you review that too? 
Yes. We assess both on-premises Active Directory and hybrid Azure AD (Entra ID) environments, including Azure AD Connect configurations and related cloud identity settings. If you are fully cloud-native on Entra ID, we can scope an assessment for that environment as well.
Will we receive help interpreting and acting on the findings?
Absolutely. Our team is available to walk your IT and security staff through the findings report, answer technical questions, and provide guidance on prioritizing remediation. We want your team to leave the engagement with confidence, not confusion.
How often should we perform an Active Directory security review?
We recommend at minimum once per year, and following any major infrastructure change such as mergers, acquisitions, significant AD restructuring, or after any suspected security incident. Organizations with stricter compliance requirements may benefit from more frequent reviews.

Get Started

Ready to See What Your Current Security Is Missing?

Book a short consultation with PlutoSec and get a practical view of where your current security model may be exposed.
Book Your Free Security Consultation