Whatsapp
Get a quote
Email Us
Call
Skip to content

Secure Your Code Before It Becomes a Risk

Secure Code Review & Vulnerability Assessment Service

Automated tools find common issues. PlutoSec's expert code reviews uncover complex vulnerabilities and provide clear, developer focused remediation guidance.

  • GWAPT Certified Reviewers

    Application security specialists auditing your code.

  • Line by Line Review

    Human review catches what scanners overlook.

  • Risk Rated Findings

    Vulnerabilities ranked by exploitability and severity.

  • Strict Source Confidentiality

    Proprietary code never leaves a secure environment.

Secure Code Review & Vulnerability Assessment Service
About Us

Expert Led Code Security Reviews

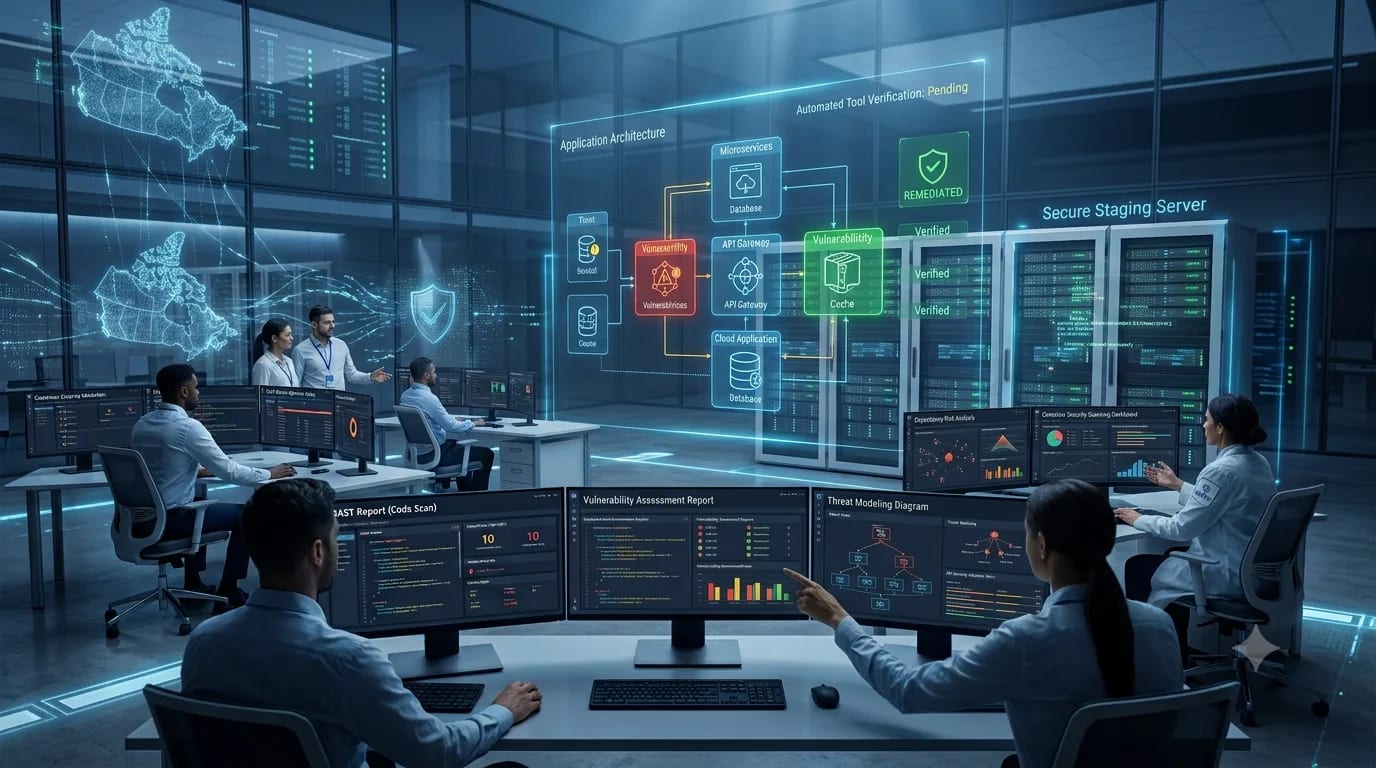
Secure code reviews help identify vulnerabilities before they become security incidents. By manually analyzing your source code, PlutoSec uncovers logic flaws, insecure coding practices, and hidden weaknesses that automated tools often miss.

Our security experts review your application against industry best practices, including OWASP and CWE standards. We provide clear, developer friendly recommendations to improve code quality, reduce risk, and strengthen your application's overall security posture.

Expert Manual Code Reviews

OWASP & CWE Aligned

Developer Focused Guidance

Stronger Application Security

Get Started

Ready to Strengthen Your Cybersecurity?

Protect your business with expert led security assessments, penetration testing, and managed security services. Talk to our specialists today.

Book a Free Consultation

Our Secure Code Review Process

  1. 1.

    Scope & Code Access

    Define the review scope and securely collect the source code.

  2. 2.

    Manual Security Analysis

    Examine the code for security flaws, logic errors, and insecure practices.

  3. 3.

    Vulnerability Validation

    Verify findings to eliminate false positives and confirm real risks.

  4. 4.

    Risk Assessment

    Prioritize vulnerabilities based on business impact and exploitability.

  5. 5.

    Detailed Reporting

    Deliver a developer friendly report with clear remediation guidance.

Why Choose PlutoSec

Your Trusted Code Security Partner

Our reviewers hold credentials including OSCP, CEH, and CISSP and bring real world offensive security experience to every engagement. That background matters because understanding how vulnerabilities get exploited is what makes a code review genuinely useful, not just a checklist exercise. We have reviewed code for financial services, healthcare, and technology companies across Canada and understand the data handling requirements that apply to your industry.

Expert Manual Code Reviews

Identify complex security vulnerabilities that automated scanners often miss.

Developer Friendly Remediation

Receive clear, actionable recommendations to fix security issues quickly.

Industry Best Practices

Reviews aligned with OWASP, CWE, and secure coding standards.

Stronger Application Security

Reduce risk and improve the security, quality, and reliability of your code.

What We Cover

Source Code Security Review

Analyze your code to identify security vulnerabilities and weaknesses.

Authentication & Access Control

Review authentication, authorization, and privilege management.

Business Logic & Input Validation

Detect logic flaws, insecure validation, and coding errors.

OWASP & CWE Vulnerabilities

Identify risks aligned with industry recognized security standards.

Secure Coding Best Practices

Evaluate code quality against secure development guidelines.

Risk Assessment & Remediation

Prioritize findings and provide practical recommendations for remediation.

Our Secure Code Review Approach

  • Analyze your source code to identify security vulnerabilities and coding weaknesses.
  • Validate findings through expert manual review to eliminate false positives.
  • Prioritize security risks based on their impact and exploitability.
  • Provide clear, developer-friendly remediation recommendations for every issue.
  • Support your team in implementing secure coding best practices.
  • Comprehensive Security Report 
  • Actionable Remediation Guidance
  • Verified Security Findings
  • Improved Code Quality

Tools & Technologies

  • Semgrep
  • SonarQube
  • Checkmarx
  • CodeQL
  • OWASP Top 10
  • CWE Top 25
  • NIST SP 800-53
  • ASVS

Get Started

Ready to Strengthen Your Cybersecurity?

Protect your business with expert led security assessments, penetration testing, and managed security services. Talk to our specialists today.

Book a Free Consultation

Why Secure Code Reviews Matter

Detect Vulnerabilities Early

Identify security flaws before they reach production.

Reduce Cybersecurity Risks

Minimize the chances of exploitation and data breaches.

Strengthen Secure Coding

Improve code quality by following security best practices.

Protect Sensitive Data

Safeguard customer and business information from security threats.

CLIENT VOICES

What our clients say

5.0 / 5based on 20 verified reviews
GoodFirms

Their team conducted a thorough security assessment and penetration testing of our website, keeping us informed throughout the process. What really stood out was how they presented technical findings in straightforward language rather than jargon — our entire team could understand the vulnerabilities and risks without needing to decode complex terminology. The final report included practical remediation recommendations we could actually implement.

Rachel CohenOwner, StantVerified
GoodFirms

Their team used a hands-on approach to identify vulnerabilities and security weaknesses that automated scans had missed, risks that could have exposed sensitive user information. Each finding was clearly explained, prioritized by severity, and paired with practical remediation recommendations. They remained available to answer questions and guide us through remediation.

Adam KowalskiOwner, Viva-menteVerified
GoodFirms

Their team took the time to understand our sustainability platform, performed a thorough security assessment, and kept us informed throughout the engagement. The final report clearly prioritized each finding and included practical remediation steps that our technical team was able to implement without confusion, significantly improving our platform's security posture.

Luca MorettiIT Security Manager, GEA.viteVerified
GoodFirms

Their team conducted a thorough penetration test and security assessment, identified vulnerabilities across our infrastructure, and provided clear, actionable steps to address them. Communication was professional and responsive throughout, and the final report was detailed yet easy to understand without unnecessary technical jargon. We especially appreciated their hands-on approach and meticulous attention to detail.

Maya EllingtonIT Manager, Pescara Blu B&BVerified
GoodFirms

Their team strengthened our cloud infrastructure, improved our access controls, and addressed security risks while providing ongoing monitoring. Communication was consistently clear, their support was responsive whenever we needed it, and their recommendations were practical and straightforward to implement.

Julian MercerIT and Cybersecurity Director, NovellowinesVerified
GoodFirms

Their team uncovered vulnerabilities in our web application that we would have missed and explained each one clearly with practical remediation steps. They stayed responsive throughout the engagement and made the entire process straightforward.

Wyatt CallahanCEOVerified
GoodFirms

Their team continuously monitored our hospitality operations for vulnerabilities and threats, flagging potential issues early with clear recommendations before problems escalated. They were responsive and knowledgeable, making security guidance practical and actionable for our specific needs. They've become a trusted partner we rely on.

Riley EastwoodIT Manager, CrodadalagoVerified
GoodFirms

Their team conducted a thorough penetration test and vulnerability assessment of our web environment, uncovering vulnerabilities we'd missed entirely. They communicated findings clearly, provided practical remediation guidance we could actually implement, and remained professional and responsive throughout the engagement.

Ava WhitmoreDirector of IT Operations, IlpassaggioVerified
GoodFirms

Working with PlutoSec was smooth and professional from start to finish. Their team manually tested our WordPress website, clearly explained each vulnerability they found, and gave us actionable steps to fix them, which made remediation straightforward instead of overwhelming. They were responsive to our questions and guided us through the process.

Sara MahmoudCTO, Andrea BaccoliniVerified
GoodFirms

Their team took time to understand our website, conducted a thorough security assessment and penetration test, then clearly explained each vulnerability they found. They provided practical remediation guidance we could actually implement to address the findings and strengthen our defenses. Communication was responsive throughout, and we felt confident in their technical knowledge and approach.

Aisha RahmanIT Security Manager, IlmiobeautyVerified
GoodFirms

Their team conducted a detailed penetration test and vulnerability assessment, identifying security weaknesses and clearly explaining the business risks behind each finding. What impressed us most was their hands-on approach — they manually validated vulnerabilities rather than relying solely on automated scanning. Beyond the initial assessment, their managed security services helped us maintain stronger ongoing security.

Zoya KhanCTO, FProgettiVerified
GoodFirms

Their manual penetration testing caught vulnerabilities that automated scanners had missed, and their final report was detailed with practical remediation recommendations we could actually implement. The team demonstrated strong technical expertise and remained responsive throughout the project, answering our questions during remediation and completing everything on schedule.

Adam Al-MasriIT Manager, FoggiaitVerified
GoodFirms

PlutoSec provided proactive managed security, vulnerability management, and ongoing monitoring that meaningfully strengthened our security posture. The team was responsive and professional, addressing concerns quickly and giving us confidence that our systems and business data are properly protected.

AnonymousVerified clientVerified
GoodFirms

Their team helped us improve IT security, system reliability, and day-to-day support, while always being responsive when we needed assistance. We especially appreciated their practical approach, clear communication, and cybersecurity knowledge.

AnonymousVerified clientVerified
GoodFirms

Their cybersecurity team took time to understand our environment and performed a detailed penetration test, going beyond automated tools to manually validate findings and explain the potential business impact clearly. The final report was well-structured with practical remediation recommendations our team could easily follow.

AnonymousVerified clientVerified

Insights & Research

ThreatResearch,CVEAnalysis,andSecurityGuides

Hands on analysis from our engineers, current vulnerabilities, emerging attack patterns, and the security decisions shaping enterprise risk in 2026.

1 min readJun 5, 2025By Admin

Managed Firewall Services for Enhanced Network Defense

Managed Firewall Services protect your network by monitoring and blocking threats, keeping your data safe and systems secure around the clock.

Read article
1 min readJun 11, 2025

Cloud Security Services to Safeguard AWS, Azure & Google Cloud

Protect your data with expert Cloud Security Services—secure infrastructure, prevent threats, and ensure compliance across all platforms.

Read
1 min readJun 11, 2025

IoT Security Testing Services to Protect Connected Devices

Secure your connected devices with expert IoT testing. Detect hidden risks early and protect your systems from evolving cyber threats.

Read

Frequently asked questions

Answers to the questions we hear most. Still unsure how it applies to your environment? Our engineers are happy to talk it through.

What is a secure code review Service?
A secure code review is a manual and automated assessment of source code to identify security vulnerabilities, coding flaws, and insecure practices before an application is deployed.
Why is secure code review important?
Secure code reviews help detect vulnerabilities early, reduce security risks, improve code quality, and prevent attackers from exploiting weaknesses in your application.
What types of vulnerabilities can a code review identify?
A secure code review can identify authentication flaws, authorization issues, input validation errors, insecure data handling, business logic flaws, hardcoded secrets, and other security weaknesses.
Do you perform manual or automated code reviews?
We combine expert manual code reviews with automated security analysis to identify both common vulnerabilities and complex security issues that automated tools may miss.
Can you review existing applications as well as new projects?
Yes. We perform secure code reviews for both existing applications and software that is still under development to identify vulnerabilities at any stage of the development lifecycle.
How can PlutoSec help improve application security?
PlutoSec identifies hidden security vulnerabilities, provides practical remediation guidance, and helps development teams build secure, resilient applications while reducing long term security risks.

Get Started

Ready to See What Your Current Security Is Missing?

Book a short consultation with PlutoSec and get a practical view of where your current security model may be exposed.
Book Your Free Security Consultation