Whatsapp
Get a quote
Email Us
Call
Skip to content

Privacy Impact Assessment (PIA) Services in Canada

Privacy Impact Assessment (PIA) Services In Canada

Launching something new that touches personal information? PlutoSec runs the privacy impact assessment that finds risks early, documents your decisions, and gives Canadian regulators a report they can follow.

  • Privacy Certified Analysts

    CIPP/C and CIPM professionals lead each review.

  • Canadian Law Mapping

    Findings tied to federal and provincial requirements.

  • Decision Ready Reporting

    Risk ratings leadership can act on.

  • Confidential Project Details

    Everything we see stays under strict NDA.

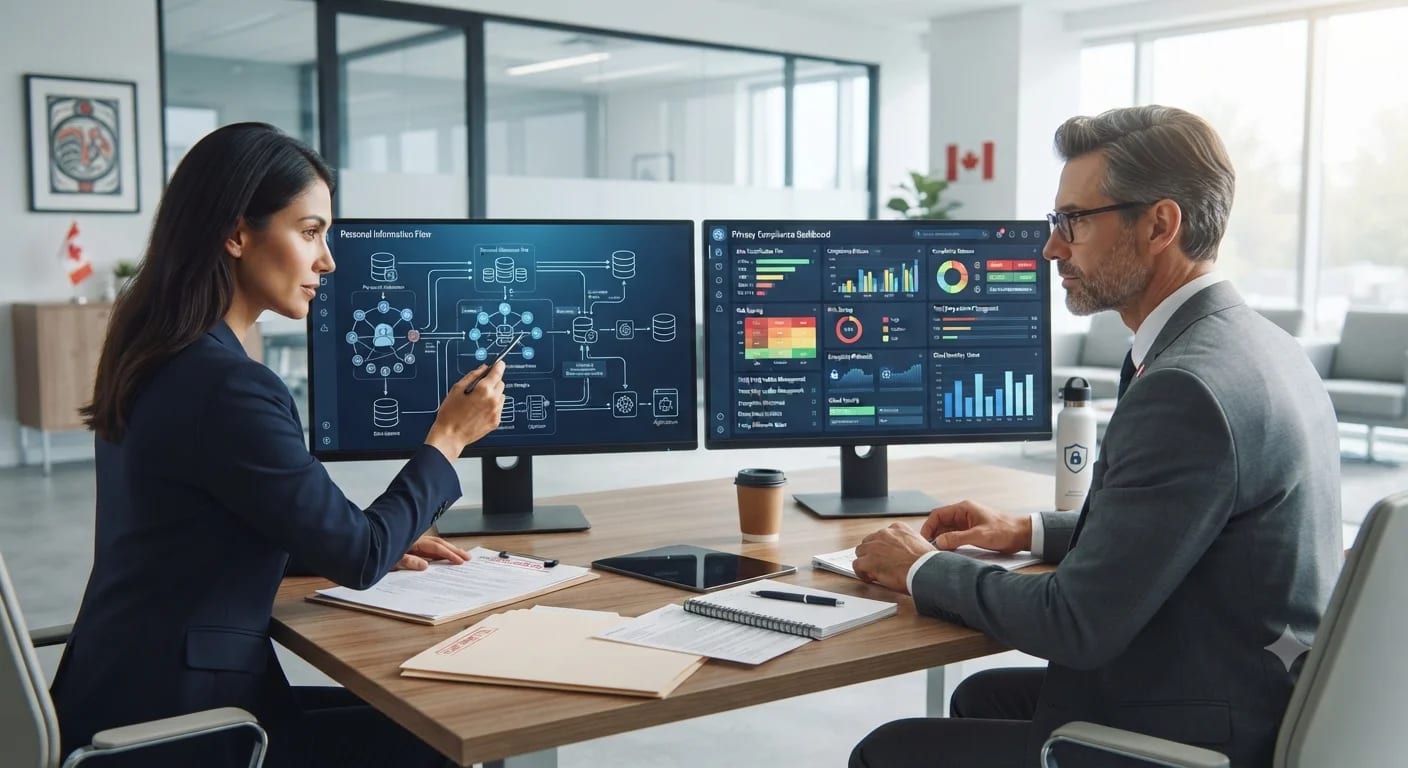
PlutoSec team reviewing personal information data flows during a privacy impact assessment engagement
About PIA

Experts in Privacy Impact Assessments

Privacy impact assessments are structured reviews that find privacy risks before personal information is collected, used, or shared. PlutoSec studies your project, maps the data involved, and shows where safeguards, notice, or consent fall short of what the law expects.

Our privacy impact analysis follows Privacy Commissioner guidance, PIPEDA, and the provincial rules that apply to you, including Quebec's Law 25 and Ontario's FIPPA. You get practical recommendations, not a template.

ISO/IEC 29134 Aligned Method

Evidence Based Findings

Privacy Risk Scoring and Treatment

Submission Ready Reports

Get Started

Ready to Strengthen Your Cybersecurity?

Protect your business with expert led security assessments, penetration testing, and managed security services. Talk to our specialists today.

Book a Free Consultation

How We Conduct Your PIA

  1. 1.

    Threshold Assessment and Scoping

    We confirm whether a PIA is required for your project, under which law, and how deep the assessment needs to go.

  2. 2.

    Data Flow Mapping

    We document what personal information is collected, why, where it moves, who can access it, and where it is stored. 

  3. 3.

    Risk and Privacy Principle Analysis

    We test the initiative against core privacy principles and legal requirements and flag every gap we find.

  4. 4.

    Mitigation Planning 

    We recommend specific technical, administrative, and contractual fixes for each risk, ranked by priority.

  5. 5.

    Report Drafting and Submission

    We write the PIA report in the format your regulator expects, and support you through submission to the OPC, OIPC, or relevant body. 

WHY CHOOSE PLUTOSEC

Privacy Reviews Backed by Real Technical Testing

Most PIA providers write policy. We do that too, but we also know how to look inside the system itself. Our team combines certified privacy and security expertise, so the risks we flag are based on how your data actually flows and where it is actually exposed, not just on what a questionnaire says. 

Security Engineers, Not Just Privacy Generalists

We test the systems behind your PIA, not just the paperwork describing them

Multi Jurisdiction Experience

PIPEDA, Alberta's POPA, HIA, and PIPA, Ontario's PHIPA, and BC's FIPPA, handled by people who work in all of them.

Reports Regulators Actually Accept

Our PIA reports follow the format and level of detail the OPC and provincial commissioners expect.

Practical, Prioritized Mitigation

You get a ranked list of fixes, not a hundred flagged risks with no direction.

What Our Privacy Impact Assessment Covers

Data Flow & Mapping Assessment

Map how personal and sensitive data is collected, processed, stored, and shared.

Privacy Risk Assessment

Identify privacy risks associated with systems, applications, processes, and data handling.

PII & Sensitive Data Review

Evaluate how personally identifiable and sensitive information is accessed and protected.

Third Party Privacy Assessment

Assess privacy risks from vendors, service providers, and external data sharing activities.

Privacy Compliance Gap Analysis

Review privacy controls against applicable laws, regulations, and organizational requirements.

Remediation & Risk Mitigation

Provide practical recommendations to reduce privacy risks and strengthen data protection.

A Methodology Built on Recognized Privacy Standards

  • Threshold assessment first, so you only pay for the depth of review your project actually needs
  • Every finding tied to a specific privacy principle or legal requirement, not a vague risk score
  • Plain language reporting your privacy officer, your executive team, and your regulator can all read
  • Ongoing support through regulator questions, resubmissions, and project changes 
  • Regulator Ready PIA Report 
  • Data Flow Diagrams 
  • Risk Register with Prioritised Mitigations
  • Executive Summary for Leadership Sign Off

Standards, Laws & Certifications Behind Our Assessments

  • ISO/IEC 29134 
  • PIPEDA
  • TBS Directive on Privacy Impact Assessment 
  • Alberta POPA, HIA & PIPA 
  • Ontario PHIPA 
  • NIST Privacy Framework 
  • CIPP/C Certified Advisors
  • CISSP

Get Started

Ready to Strengthen Your Cybersecurity?

Protect your business with expert led security assessments, penetration testing, and managed security services. Talk to our specialists today.

Book a Free Consultation

Why a Privacy Impact Assessment Matters

Avoid Regulatory Delays or Stop Work Orders

Regulators can pause or order changes to a project that skipped a required PIA.

Prevent Costly Privacy Breaches

The gaps a PIA surfaces are often the same gaps that lead to a breach later.

Protect Public and Customer Trust

Being able to show privacy was considered upfront matters to clients, patients, and citizens alike.

Build Privacy Into the Project, Not Bolted On After

Fixing a design flaw before launch is far cheaper than retrofitting it once the system is live.

CLIENT VOICES

What our clients say

5.0 / 5based on 20 verified reviews
GoodFirms

Their team conducted a thorough security assessment and penetration testing of our website, keeping us informed throughout the process. What really stood out was how they presented technical findings in straightforward language rather than jargon — our entire team could understand the vulnerabilities and risks without needing to decode complex terminology. The final report included practical remediation recommendations we could actually implement.

Rachel CohenOwner, StantVerified
GoodFirms

Their team used a hands-on approach to identify vulnerabilities and security weaknesses that automated scans had missed, risks that could have exposed sensitive user information. Each finding was clearly explained, prioritized by severity, and paired with practical remediation recommendations. They remained available to answer questions and guide us through remediation.

Adam KowalskiOwner, Viva-menteVerified
GoodFirms

Their team took the time to understand our sustainability platform, performed a thorough security assessment, and kept us informed throughout the engagement. The final report clearly prioritized each finding and included practical remediation steps that our technical team was able to implement without confusion, significantly improving our platform's security posture.

Luca MorettiIT Security Manager, GEA.viteVerified
GoodFirms

Their team conducted a thorough penetration test and security assessment, identified vulnerabilities across our infrastructure, and provided clear, actionable steps to address them. Communication was professional and responsive throughout, and the final report was detailed yet easy to understand without unnecessary technical jargon. We especially appreciated their hands-on approach and meticulous attention to detail.

Maya EllingtonIT Manager, Pescara Blu B&BVerified
GoodFirms

Their team strengthened our cloud infrastructure, improved our access controls, and addressed security risks while providing ongoing monitoring. Communication was consistently clear, their support was responsive whenever we needed it, and their recommendations were practical and straightforward to implement.

Julian MercerIT and Cybersecurity Director, NovellowinesVerified
GoodFirms

Their team uncovered vulnerabilities in our web application that we would have missed and explained each one clearly with practical remediation steps. They stayed responsive throughout the engagement and made the entire process straightforward.

Wyatt CallahanCEOVerified
GoodFirms

Their team continuously monitored our hospitality operations for vulnerabilities and threats, flagging potential issues early with clear recommendations before problems escalated. They were responsive and knowledgeable, making security guidance practical and actionable for our specific needs. They've become a trusted partner we rely on.

Riley EastwoodIT Manager, CrodadalagoVerified
GoodFirms

Their team conducted a thorough penetration test and vulnerability assessment of our web environment, uncovering vulnerabilities we'd missed entirely. They communicated findings clearly, provided practical remediation guidance we could actually implement, and remained professional and responsive throughout the engagement.

Ava WhitmoreDirector of IT Operations, IlpassaggioVerified
GoodFirms

Working with PlutoSec was smooth and professional from start to finish. Their team manually tested our WordPress website, clearly explained each vulnerability they found, and gave us actionable steps to fix them, which made remediation straightforward instead of overwhelming. They were responsive to our questions and guided us through the process.

Sara MahmoudCTO, Andrea BaccoliniVerified
GoodFirms

Their team took time to understand our website, conducted a thorough security assessment and penetration test, then clearly explained each vulnerability they found. They provided practical remediation guidance we could actually implement to address the findings and strengthen our defenses. Communication was responsive throughout, and we felt confident in their technical knowledge and approach.

Aisha RahmanIT Security Manager, IlmiobeautyVerified
GoodFirms

Their team conducted a detailed penetration test and vulnerability assessment, identifying security weaknesses and clearly explaining the business risks behind each finding. What impressed us most was their hands-on approach — they manually validated vulnerabilities rather than relying solely on automated scanning. Beyond the initial assessment, their managed security services helped us maintain stronger ongoing security.

Zoya KhanCTO, FProgettiVerified
GoodFirms

Their manual penetration testing caught vulnerabilities that automated scanners had missed, and their final report was detailed with practical remediation recommendations we could actually implement. The team demonstrated strong technical expertise and remained responsive throughout the project, answering our questions during remediation and completing everything on schedule.

Adam Al-MasriIT Manager, FoggiaitVerified
GoodFirms

PlutoSec provided proactive managed security, vulnerability management, and ongoing monitoring that meaningfully strengthened our security posture. The team was responsive and professional, addressing concerns quickly and giving us confidence that our systems and business data are properly protected.

AnonymousVerified clientVerified
GoodFirms

Their team helped us improve IT security, system reliability, and day-to-day support, while always being responsive when we needed assistance. We especially appreciated their practical approach, clear communication, and cybersecurity knowledge.

AnonymousVerified clientVerified
GoodFirms

Their cybersecurity team took time to understand our environment and performed a detailed penetration test, going beyond automated tools to manually validate findings and explain the potential business impact clearly. The final report was well-structured with practical remediation recommendations our team could easily follow.

AnonymousVerified clientVerified

Insights & Research

ThreatResearch,CVEAnalysis,andSecurityGuides

Hands on analysis from our engineers, current vulnerabilities, emerging attack patterns, and the security decisions shaping enterprise risk in 2026.

1 min readMay 30, 2025By Admin

Reliable API Security Testing Services to Prevent Data Leaks

Plutosec offers expert API security testing to prevent data leaks, meet compliance, and secure every endpoint with real-time threat detection.

Read article
1 min readJun 4, 2025

Rapid Cyber Emergency Response Services to Minimize Downtime

Rapid and efficient cyber emergency response services are designed to quickly detect, contain, and recover from cyberattacks—minimizing downtime and safeguarding your business operations.

Read
1 min readMay 27, 2025

Comprehensive Vulnerability Assessment to Strengthen Your Network

Many networks hold hidden flaws that remain unnoticed until damage strikes. A Vulnerability assessment check shows those risks early.

Read

Frequently asked questions

Answers to the questions we hear most. Still unsure how it applies to your environment? Our engineers are happy to talk it through.

What is a privacy impact assessment (PIA)?
A privacy impact assessment is a formal review of how a project, system, or service collects, uses, stores, and shares personal information, and whether that handling is lawful, proportionate, and properly secured. In plain terms, a PIA answers one question: does this initiative respect people's privacy, and if not, what needs to change before it goes live. 
What is the purpose of a privacy impact assessment?
The purpose of a privacy impact assessment is to catch privacy risk early, while a project can still be redesigned cheaply, rather than after launch when fixing a problem is expensive and a breach or complaint has already happened. It also gives your organization a documented record showing regulators, auditors, and customers that privacy was considered from the start. 
Is a privacy impact assessment mandatory in Canada?
It depends on who you are. Federal government institutions must complete a PIA under the Treasury Board Directive on Privacy Impact Assessment and submit it to the Office of the Privacy Commissioner of Canada. Private-sector organizations under PIPEDA are not legally required to complete one, though the OPC recommends it as best practice, and several provinces impose their own mandatory requirements on public bodies and health custodians. 
Do I need a privacy impact assessment in Alberta?
Public bodies in Alberta must complete a PIA under POPA, the province's public sector privacy law, in specific circumstances, and health custodians must submit one under the HIA before implementing a new system or practice involving health information. Private-sector organizations governed by Alberta's PIPA are not required to complete a PIA, but the OIPC encourages it whenever personal information handling carries meaningful risk.
Can I just use a privacy impact assessment template?
A template is a useful starting point, but it will not tell you which sections apply to your specific project, what your regulator expects to see, or how to word your risk analysis so it holds up under review. We use standard templates as a foundation, then tailor the content, evidence, and technical detail to your actual systems.

Get Started

Ready to See What Your Current Security Is Missing?

Book a short consultation with PlutoSec and get a practical view of where your current security model may be exposed.
Book Your Free Security Consultation