Identity & Access Management
We review your users, roles, groups, trust policies, and permissions to design recommendations that mitigate privileges creep and privilege escalation.

Secure Your AWS Cloud with Confidence
How secure is your infrastructure on the AWS cloud? Automated scanners only tell very little. With our AWS Cloud Security Assessment, you’ll get an in-depth review by AWS Certified Security Specialty engineers to evaluate your IAM, networking, storage permissions, and workloads against AWS best practices and Canadian regulatory requirements. We’ll identify and prioritize issues for remediation based on severity.
AWS Certified Security Specialty consultants with deep experience securing Canadian cloud workloads.
We test IAM policies, S3 permissions and EC2 configurations the way real adversaries exploit them.
Every finding comes with a fix mapped to the AWS Well Architected security pillar.
Your AWS environment details remain protected under strict confidentiality and access controls.
AWS affords your organization great flexibility, and that flexibility is precisely where risk hides in the cloud. Overly permissive IAM roles, publicly accessible S3 buckets, unrestricted security groups, and unmonitored API activity are some of the most common findings we uncover in the Canadian AWS environment, often in organizations that believed their setups were secure.
Our engineers manually trace IAM trust relationships, look for privilege escalation opportunities, and validate that your AWS security groups are doing what you think they're doing. We scope each assessment based on your environment, your compliance requirements and your risk tolerance, and deliver findings your team can act on.
INDUSTRIES WE SERVE
From regulated industries to critical infrastructure, our assessments are scoped for your sector's specific threats and compliance requirements.
Get Started
Protect your business with expert led security assessments, penetration testing, and managed security services. Talk to our specialists today.
We discuss your AWS environment, account structure and the compliance frameworks you need to align with
You provide scoped down read only IAM credentials, we will never make changes to your production environment.
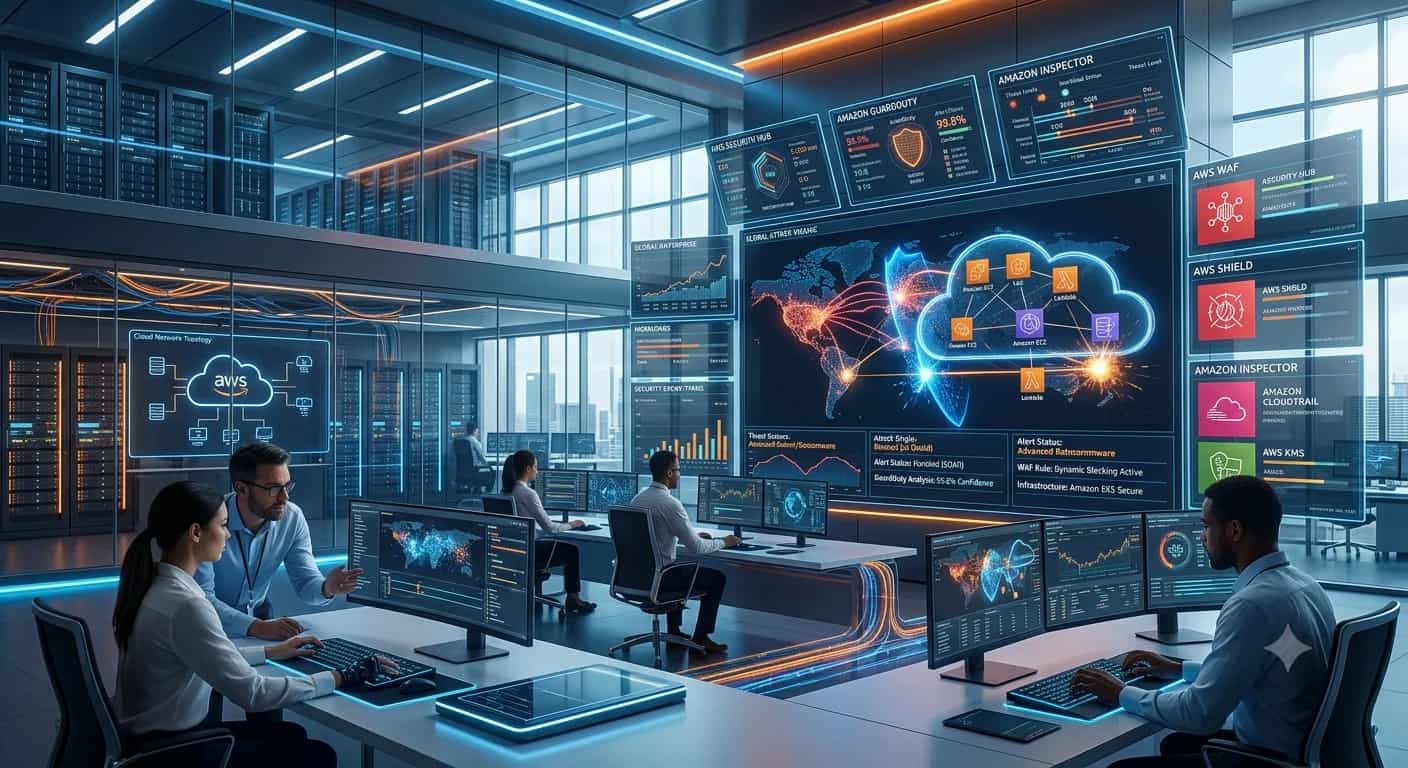
Our engineers will perform a manual assessment of your IAM, VPC, S3, EC2, databases, and serverless workloads, using GuardDuty, Security Hub and IAM Access Analyzer to assist the assessment
You will receive a technical report for your engineering team and executive summary report including alignment to relevant compliance frameworks
Why Choose PlutoSec
Most providers offer a cloud security scanner, they run it, export the results, and call that an assessment. We take it a step further. Our AWS certified engineers review each result manually so you can rest assured that there are no false positives or negatives.
Every assessment is led by consultants with AWS Security Specialty certification, as well as CCSP, CISSP, and ISO 27001 Lead Implementer qualifications.
All findings are mapped to SOC 2, ISO 27001, PCI DSS, PHIPA, NIST CSF, and CCCS/ITSG-33 standards.
We always operate under scoped, read only IAM credentials and sign an NDA prior to scoping.
We offer a free retest after your team has addressed all findings reported in your assessment report.
We review your users, roles, groups, trust policies, and permissions to design recommendations that mitigate privileges creep and privilege escalation.
We evaluate your Virtual Private Cloud designs, including your routing tables, NACLs, AWS Security Groups, to identify Least Privilege violations.
We test your Amazon S3 usage for publicly available data and misconfigured buckets, as well as the encryption of sensitive data.
We analyze Amazon Elastic Compute Cloud instances in terms of individual configuration and the overall patching strategy. We also evaluate access control at the level of instances.
We examine Amazon RDS and DynamoDB databases and other managed database services for exposure and privilege control issues.
We assess your Amazon Elastic Kubernetes Service, Amazon Elastic Container Service, AWS Lambda functions, and associated AWS Identity and Access Management roles and function-level permissions.
What You Get
Get Started
Protect your business with expert led security assessments, penetration testing, and managed security services. Talk to our specialists today.
Focus on securing the infrastructure that your business is built upon before an adversary can.
Focus on detecting misconfigurations and privileges within your AWS environment that create attack surfaces.
Ensure that your storage and databases are appropriately hardened and secured around sensitive data.
Understand your SOC 2 ISO 27001, PCI DSS, PHIPA, NIST CSF and ITSG-33 control sets mapping to your cloud environment.
Insights & Research
Hands on analysis from our engineers, current vulnerabilities, emerging attack patterns, and the security decisions shaping enterprise risk in 2026.
Cyber threats grow stronger and more frequent every day. You use the internet more than before. Hackers target your data through attacks, ransomware, and fake emails.
Read articleFAQ
Answers to the questions we hear most. Still unsure how it applies to your environment? Our engineers are happy to talk it through.
Get Started
Book a short consultation with PlutoSec and get a practical view of where your current security model may be exposed.